Send the exact assignment or rubric from your classroom and a custom sample written to it lands in 24 to 48 hours, the first one free. IT-FPX4073 is Capella’s Organizational Security course. It centers on assessing an organization's security posture as ranked risk to the assets its operations cannot run without. Searches like "it fpx 4073 assessment 3 assignment example", "ITFPX4073 sample paper", and "IT-FPX4073 assessment samples" land on this page.
What IT-FPX4073 is really about
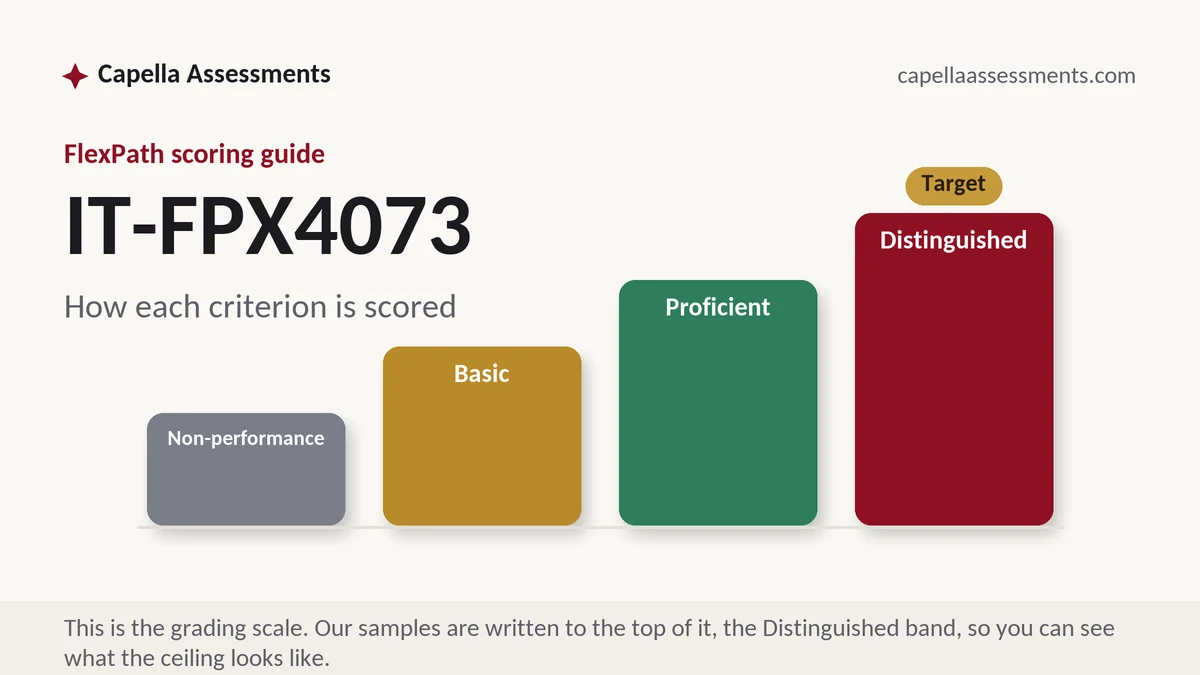
IT-FPX4073 is scored on a chain most first drafts skip: asset, threat, likelihood, impact, control. The assessments hand you an organization, and the criteria want to know what it values before they want to know what threatens it, because a threat only means something against a named asset. Strong submissions therefore start from the business: the systems revenue moves through, the data a regulator cares about, the people who hold the process together. Each risk is then rated, not listed, and the rating is defended with a likelihood and an impact a manager could argue with. A finding without a severity is an observation; a finding without an owner is a wish, and the scoring guide treats both that way.
Controls are the second half, and they are scored on proportion. Recommending encryption everywhere and training for everyone is the security equivalent of prescribing rest, technically defensible and useless to the organization deciding what to fund first. The criteria typically want controls matched to the risks just rated, sequenced by severity, and costed at least in effort, because the deliverable is meant to survive contact with a budget. Physical and personnel measures belong in the same register as technical ones; the course treats a propped door and a shared password as the same category of failure. Where a framework is named, it is used to organize the assessment rather than quoted for authority, and the organization's size decides how much of it applies.
What IT-FPX4073’s assessments ask for
Assessments in current courserooms generally follow the shape of a real engagement. First comes the inventory and threat analysis: what the organization runs, what could plausibly go wrong, and which combinations deserve attention. Then the risk assessment proper, where each threat-asset pair gets a likelihood, an impact and a resulting severity you can defend. The final stretch usually asks for a mitigation program: controls mapped to the ranked risks, an order of implementation, and the residual risk the organization is being asked to accept in writing. Where the scenario includes an incident, the criteria want it read as evidence about the posture rather than as a story, and where budget appears, they want the expensive control justified against the cheap one it beat.
Where students lose points in IT-FPX4073
The classic loss is the threat catalog: every attack the textbook names, described accurately, attached to nothing the scenario organization actually owns. Second is the flat risk register, where everything is rated high because rating requires a defended judgment and high feels safe; a register with no spread has made no decisions. Third is the control dump, mitigations listed alphabetically rather than mapped to the risks that justify them. Marks also go for severities with no stated basis, for owners never assigned, for residual risk left unmentioned as though controls end the matter, and for assessing the generic enterprise rather than the organization the scenario describes, which reads as thorough and scores as off-target.
The IT-FPX4073 drawers
IT-FPX4073 Assessment 1 threat and asset analysis example
Assessment 1 typically inventories what the organization depends on and what plausibly threatens it. On request, free, 24-48h.
IT-FPX4073 Assessment 2 risk assessment example
Assessment 2 often rates each threat-asset pair with a severity you must defend. On request, free, 24-48h.
IT-FPX4073 Assessment 3 mitigation program example
Assessment 3 usually maps controls to ranked risks with owners and an implementation order. On request, free, 24-48h.
Your classroom shows something else?
Capella University revises courses; assessment counts and deliverables shift between terms. Send what your classroom shows and the desk matches it exactly.
Using a IT-FPX4073 sample the right way
Use a sample to see how a defended rating reads. Find one risk and follow it: the asset it threatens, the likelihood claimed, the impact claimed, the severity that falls out, and the control that answers it with a named owner. That thread is the whole course in miniature. Then build your register from the scenario in your courseroom, because the asset list is where all the marks start and yours will differ. Sections vary in what they emphasize; a sample written to your exact instructions and scoring guide costs nothing the first time and lands within 24-48h.
How these samples are written
Every sample in this drawer is written the same way our custom ones are: the scoring guide decoded criterion by criterion, a subject-matched writer drafting to the Distinguished column, APA checked line by line, and the reasoning annotated so the paper teaches while it shows. Capella revises scoring guides, so a custom request is always written to the guide in YOUR courseroom, never from a stale template.
IT-FPX4073 questions, answered
How do I rate likelihood without real data?
State a basis and commit. Industry patterns, the scenario's own history, and the exposure the architecture creates all count as bases; the criteria are testing whether your judgment is defensible, not whether it matches a table. A likelihood with a stated reason can be argued with, which is the point. What fails is a rating that appears from nowhere or a register where every cell reads the same.
Is there an IT-FPX4073 Assessment 2 sample available?
Yes; ask for it through the request form and it is free the first time. Because sections build the risk assessment on different scenario organizations, send your own instructions and scoring guide with the request, and the sample will be assembled to those within 24-48h. Reading one built for a different scenario still shows the rating structure, but yours will fit what your criteria actually measure.
Do physical and personnel risks really belong in an IT paper?
In this course, yes, and leaving them out is a scored omission rather than a stylistic choice. The organization is the unit of analysis, so a propped server room door, a departing administrator and an unpatched host are all entries in the same register. Sections differ in emphasis, but the criteria usually ask for the posture as a whole, not the network alone.